
Designing PCB electronics for reliable brownout recovery means controlling what happens before, during and after the supply leaves its valid operating range. A board that restarts after a clean power cycle can still fail during a shallow dip, a slow voltage collapse or repeated attempts to start from a current-limited supply.
For industrial controllers, robotic equipment and connected embedded products, the consequences extend beyond a processor reset. Outputs can glitch, configuration data can become inconsistent and peripherals can remain powered while the controller loses state. Reliable recovery therefore requires coordinated power architecture, reset supervision, firmware and verification.
Define successful recovery before choosing components
Start with an application-level recovery requirement. Specify the supply disturbances the product must tolerate, the functions that must remain available and the conditions under which operation may resume.
Distinguish between riding through a disturbance without interruption and entering a controlled state before restarting. These are different requirements with different energy budgets.
The safe state also needs definition. Removing drive power may be appropriate for one machine, while another needs retained control energy to complete a controlled stop. A processor reset alone does not establish either outcome.
Define acceptable data loss, output behaviour, restart time and any requirement for operator acknowledgement. Include repeated disturbances, not just a single interruption followed by a healthy supply.
Choose brownout thresholds for PCB electronics
A brownout threshold must protect the complete powered subsystem, not simply match a convenient microcontroller setting. Check minimum operating voltages for the selected clock frequency, flash operations, external memory, transceivers and analogue circuitry across the specified temperature range.
The nominal reset threshold is not the guaranteed protection boundary. Account for threshold tolerance, detection delay, reset propagation and the voltage lost while the circuit responds.
A useful first-order check for a falling rail is:
Vtrip,min - (maximum fall rate × response time) > minimum permitted operating voltage
The response time must reflect the action being protected. Asserting reset, inhibiting a write and disabling a power stage can have different timing requirements. Abrupt steps also need separate analysis because a linear fall-rate assumption may not represent them adequately.
For example, assume a subsystem needs at least 3.0 V. A hypothetical supervisor with an assertion threshold spanning 3.05 V to 3.15 V leaves only 50 mV of worst-case falling-voltage margin. Whether that is sufficient depends on the actual collapse rate and response time. The normal rail must also remain above the highest release threshold, including ripple and tolerance.
Manufacturer documentation such as the TI TPS3808 datasheet shows why threshold accuracy, timing and reset-output behaviour all need review. An external supervisor is useful only when its guaranteed behaviour matches the application.
Coordinate multiple rails and reset release
In multi-rail PCB electronics, monitoring the processor supply alone can miss the failure that matters. A controller may remain operational while its sensor supply, memory rail or gate-driver supply becomes invalid.
Determine which rails are essential for each operating state. A missing communications supply might require degraded operation, whereas loss of a feedback rail could require immediate inhibition of an actuator. Document these dependencies rather than treating every power-good signal identically.
Combine hardware fault signals where independent protection is required. Check the electrical compatibility of open-drain outputs, pull-ups and reset inputs, including what happens when one device is unpowered. An unpowered monitor must not inadvertently prevent a fault from being recognised.
Reset release needs both adequate voltage and adequate settling time. Hysteresis reduces threshold chatter, while a release delay allows rails, oscillators and peripherals to settle. Verify whether another dip restarts that delay.
Also test the interaction between restart and source capability. Re-enabling a motor drive, radio or large capacitive load can collapse the supply again, producing a reset loop. Staged load activation, controlled inrush or a defined retry policy may be necessary. A longer reset delay alone does not correct insufficient source capacity.
Size hold-up energy around a defined action
Hold-up capacitance in PCB electronics should support a specific task: bridging a brief interruption, completing an authorised memory operation or maintaining control long enough to reach the required state. It should not be selected simply because additional capacitance appears reassuring.
For an approximately constant-current load connected directly to a capacitor:
C ≥ I × t / ΔV
A 50 mA load requiring 10 ms of operation across an allowed 0.3 V drop needs approximately 1,670 µF before allowances for tolerance, effective capacitance, temperature, ageing and ESR. The immediate ESR-related voltage step also consumes part of that voltage budget.
For a regulated, approximately constant-power load, an energy calculation is usually more appropriate:
C ≥ 2 × Pout × t / [η × (Vstart² - Vend²)]
Here, efficiency is represented by η. The usable endpoint must respect converter undervoltage lockout, dropout and the minimum voltage required by downstream circuitry.
Confirm where the stored energy flows. Without suitable isolation, a collapsing input can drain the reservoir into other loads. Early warning may therefore need to monitor the upstream supply while the protected subsystem operates from its local reserve.
These decisions belong within the wider power electronics design approach for reliability, EMC and scale, including inrush, thermal stress and converter stability.
Make firmware restart from a known state
Brownout recovery in PCB electronics should not depend on firmware executing correctly after the supply has already become invalid. Hardware supervision establishes the electrical boundary; firmware manages the controlled transition back into operation.
At startup, hold application outputs in their defined state until essential dependencies have been checked. Configure output levels before enabling peripheral functions where the processor architecture allows it. Review bootloader behaviour as well as application code because both can affect pins and timing.
Assume external devices may not have reset alongside the processor. A sensor can retain its configuration, a communications controller can retain buffered traffic and a bus can remain in an interrupted transaction. Use supported reset mechanisms and bounded recovery procedures rather than waiting indefinitely for a response.
Read reset-cause information early, following the device-specific rules for retaining and clearing flags. Use it to support diagnosis, but do not make safe startup conditional on that information being complete.
A watchdog addresses stalled execution; it does not replace voltage supervision. During recovery, watchdog servicing should reflect meaningful progress, with deadlines for peripheral initialisation and communications. Otherwise, startup code can remain stuck while continuing to satisfy the watchdog.
Protect persistent data against interrupted writes
For PCB electronics that store settings, counters or calibration data, a successful reboot is insufficient if the recovered state is inconsistent. Treat non-volatile updates as transactions that can be interrupted at any instruction or memory-programming step.
A common approach uses separate records containing a format identifier, sequence information, payload and integrity check. Write and validate the replacement before retiring the previous valid record. Keep erase operations from destroying the only recoverable copy.
The exact protocol must match the memory technology. Programming granularity, erase-block size, endurance and behaviour during undervoltage differ between internal flash, EEPROM and external memories. Do not assume a multi-byte write or commit marker is atomic unless the device documentation supports that assumption.
A CRC helps detect corruption but does not, by itself, establish which record is newest or whether a transaction completed. Recovery logic needs explicit rules for incomplete records, sequence rollover and firmware-version changes.
Avoid starting a final write simply because a low-voltage interrupt occurred. That strategy requires enough guaranteed energy for detection, software latency and worst-case memory completion, with every required rail still valid. Where that cannot be demonstrated, preserve an earlier valid state instead. Acknowledgement to a host should also reflect the persistence guarantee the product actually provides.
Keep reset, sensing and interfaces electrically defined
Layout and interface details can undermine otherwise sound PCB electronics. Route voltage sensing from the intended measurement point, with a controlled reference return, rather than from a noisy switching node or a convenient location elsewhere on the rail.
Use filtering deliberately. It can reject harmless switching noise, but it also delays detection. Evaluate the complete sensing network against the shortest disturbance that must trigger protection.
Keep reset routing away from high-dv/dt switching nodes and review pull-up strength, leakage, capacitance and logic thresholds. A supervisor output is only guaranteed within its specified operating conditions. Below that range, the surrounding circuit still needs to produce acceptable behaviour.
Check every connection between independently powered domains. An energised interface can inject current through an unpowered device's protection structures, partially powering it and preventing a clean reset. Review powered-off pin ratings, injection-current limits and any required isolation or level translation.
Actuator control deserves particular attention. Processor pins may become high impedance during reset, so gate-driver enables and other critical controls need defined hardware defaults. Their behaviour must remain appropriate as individual rails decay, not just while the processor supply is nominal. Where continued controlled operation is required, the necessary control circuitry needs its own justified energy reserve.
Test realistic disturbances rather than clean power cycles
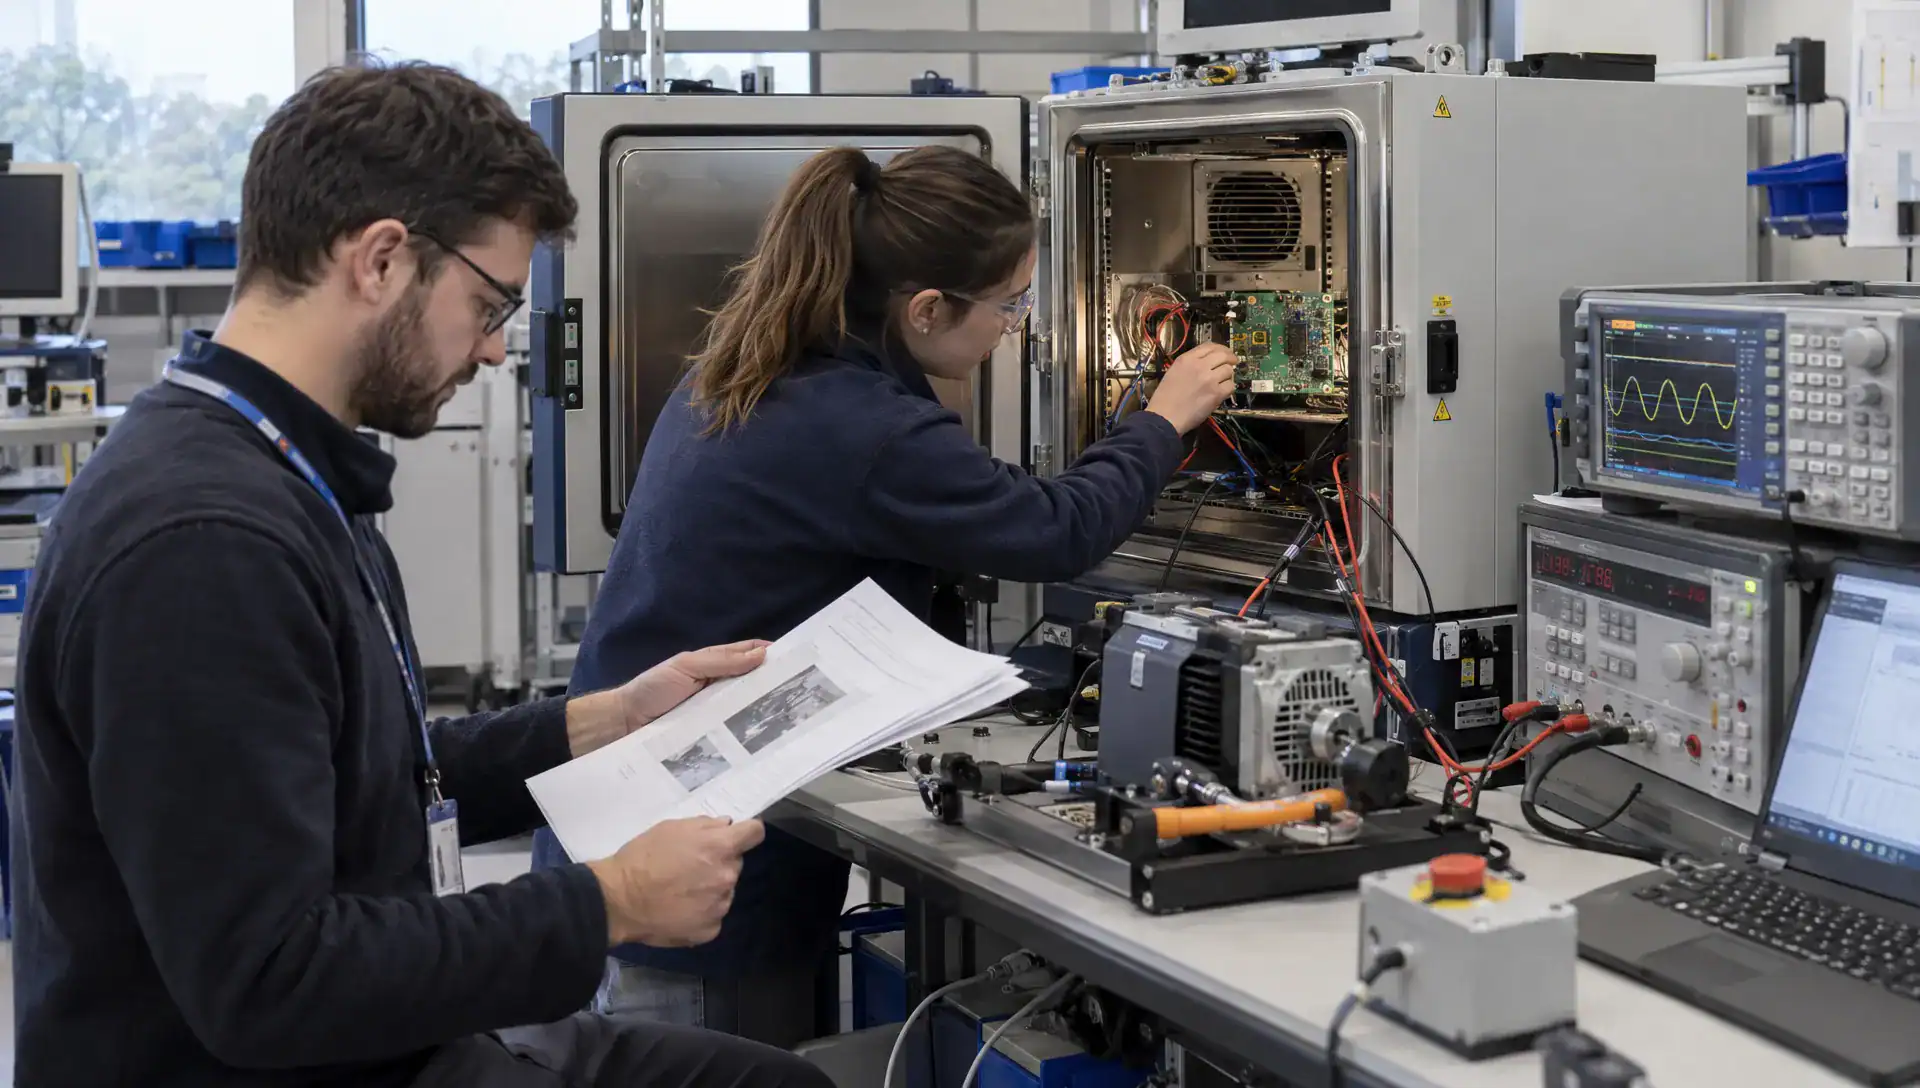
Verification of PCB electronics should reproduce the waveforms that expose uncertain states. Switching a bench supply off and on tests only a small part of the operating envelope.
Use equipment capable of generating controlled disturbances at the product input. Confirm the waveform at the connector and at relevant internal rails because cables, input filters and stored energy can substantially change what the circuitry experiences.
| Disturbance | What it can expose | Evidence to capture |
|---|---|---|
| Shallow dip near a threshold | Reset chatter or missed detection | Rail voltage and reset transitions |
| Slow voltage decay | Operation below a valid voltage or partial powering | Rail sequence and interface levels |
| Fast interruption | Detection latency and inadequate hold-up | Local rail collapse and output response |
| Repeated dips | Restart loops or incomplete initialisation | Reset history and recovery time |
| Current-limited startup | Inrush-related cycling | Input current and power-good signals |
| Dip during a memory update | Interrupted or inconsistent persistence | Recovered records and host-visible state |
| Dip during an actuator command | Unintended output behaviour | Enable, command and feedback signals |
Sweep depth, duration, repetition rate and recovery slope. Repeat at representative load and temperature extremes, including the maximum credible load during recovery.
Where applicable, IEC 61000-4-11 addresses voltage dips and interruptions at AC input power ports within its scope, while IEC 61000-4-29 addresses DC input power ports. Select the applicable product requirements and performance criteria; these references do not create a universal test profile or guarantee compliance.
Measure the complete recovery sequence
For PCB electronics, observing reset deassertion does not prove that the product has recovered. Capture the sequence from the initial disturbance through to the point where useful operation is genuinely restored.
Useful oscilloscope channels include the incoming supply, processor rail, reset, power-stage enable and a firmware timing signal. Additional captures may be needed for memory supply, communications activity or analogue reference settling. Use appropriate probing so measurement connections do not introduce misleading noise or ground shifts.
Define pass criteria before testing. Depending on the application, these could include no unintended actuator enable, preservation of the last acknowledged configuration and recovery within a specified time once stable power returns. Analogue measurements should remain flagged invalid until their references and signal chains have settled.
Trigger disturbances at different software phases. A dip during an idle loop is not equivalent to one during flash erase, network negotiation or motor acceleration. Automated repetition helps cover these timing relationships more effectively than manual power cycling.
Retain waveforms alongside firmware versions, component variants and test conditions. These records make it possible to distinguish a genuine improvement from a change in test setup.
Preserve recovery behaviour through production changes
Reliable brownout recovery in PCB electronics must survive component substitutions and later product revisions. A replacement regulator can change undervoltage lockout or soft-start behaviour. A different supervisor can change threshold tolerance, delay or output characteristics. Even a capacitor substitution can reduce usable hold-up energy.
Identify these parts as behaviour-critical in the design documentation. Define which electrical parameters an alternative must meet and which substitutions require renewed disturbance testing. Matching a footprint and nominal value is not sufficient.
Provide test access to relevant rails, reset and critical enables. Production testing does not need to repeat the full qualification programme on every unit, but it should detect assembly defects that invalidate the protection strategy. Representative deeper tests can support change validation and ongoing process control.
This is one reason to connect recovery requirements with the PCB design-for-manufacturing checklist for reliable volume builds. Testability and controlled alternatives need attention before release to manufacturing.
Keep firmware recovery tests in the regression programme. Changes to boot sequencing, clock configuration, storage handling or communications can alter behaviour even when the schematic remains unchanged.
Frequently asked questions
Is the microcontroller's internal brownout detector enough? It can be sufficient for some PCB electronics when its guaranteed thresholds, response time and reset behaviour protect every relevant operating condition. External supervision becomes useful when tighter thresholds, multiple monitored rails or independent hardware control are required. The decision needs a system-level analysis.
Can larger capacitors solve brownout problems? They can extend operating time, but they do not correct inappropriate thresholds, unsafe output defaults or interrupted data transactions. Additional capacitance can also increase inrush and prolong time spent near an undervoltage boundary. Calculate the required energy and verify the complete power sequence.
Should equipment restart automatically after power returns? That depends on the application and its risk assessment. Automatic recovery may be appropriate for a monitoring node, while machinery may require a separate restart permission. Separate processor startup from permission to resume potentially hazardous activity.
Does passing a voltage-dip test prove reliable recovery? It demonstrates behaviour under the conditions tested. Confidence also depends on covering relevant loads, temperatures, disturbance timing, component tolerances and software states. Field supply conditions and applicable product requirements should shape the verification plan.
Review brownout recovery before the design is fixed
Reliable PCB electronics need a recovery strategy that connects power behaviour, hardware defaults, embedded firmware and persistent data. Agree the required outcome first, then verify it with measured disturbances rather than assumptions about reset.
ProMicro supports electronics development across power electronics, analogue design, embedded systems, PCB layout, prototyping and manufacturing preparation. For a brownout-sensitive product, a practical starting point is a joint review of rail dependencies, protection thresholds, startup sequencing and the evidence needed to demonstrate reliable recovery.