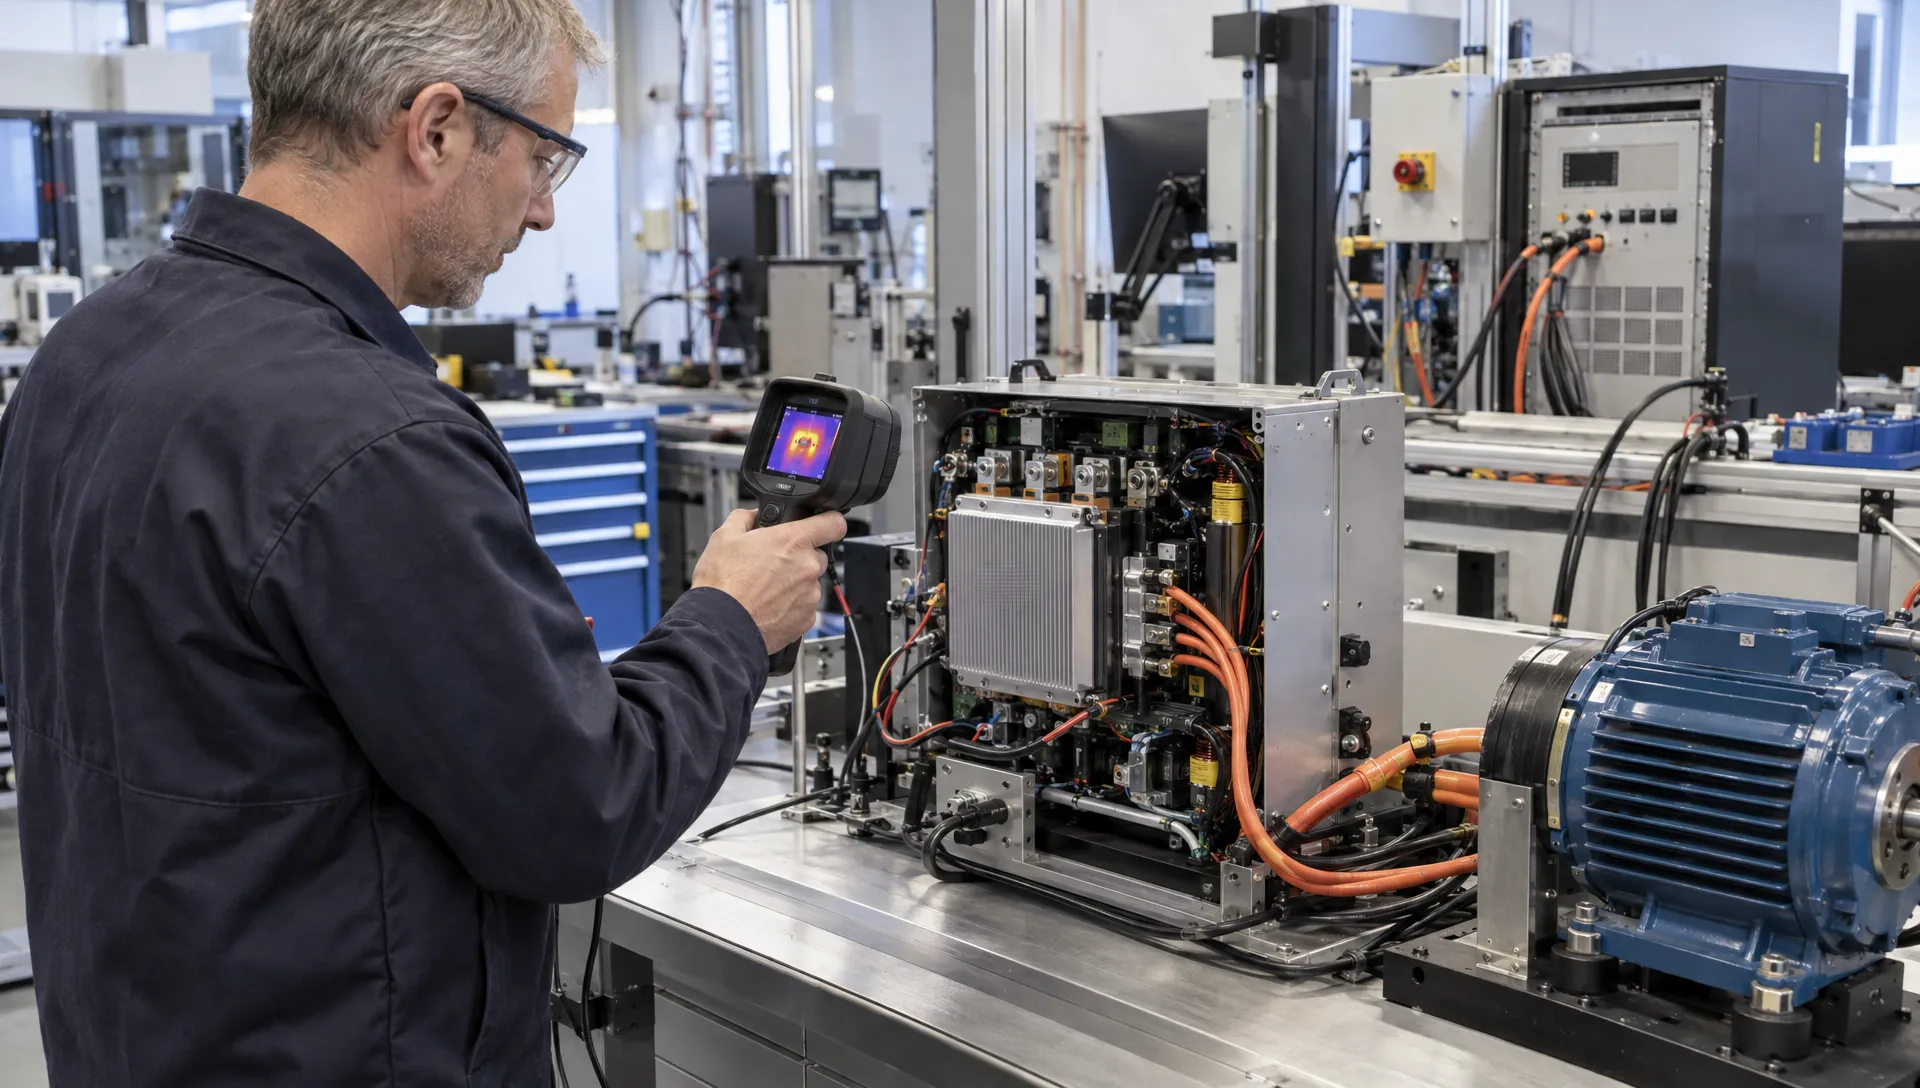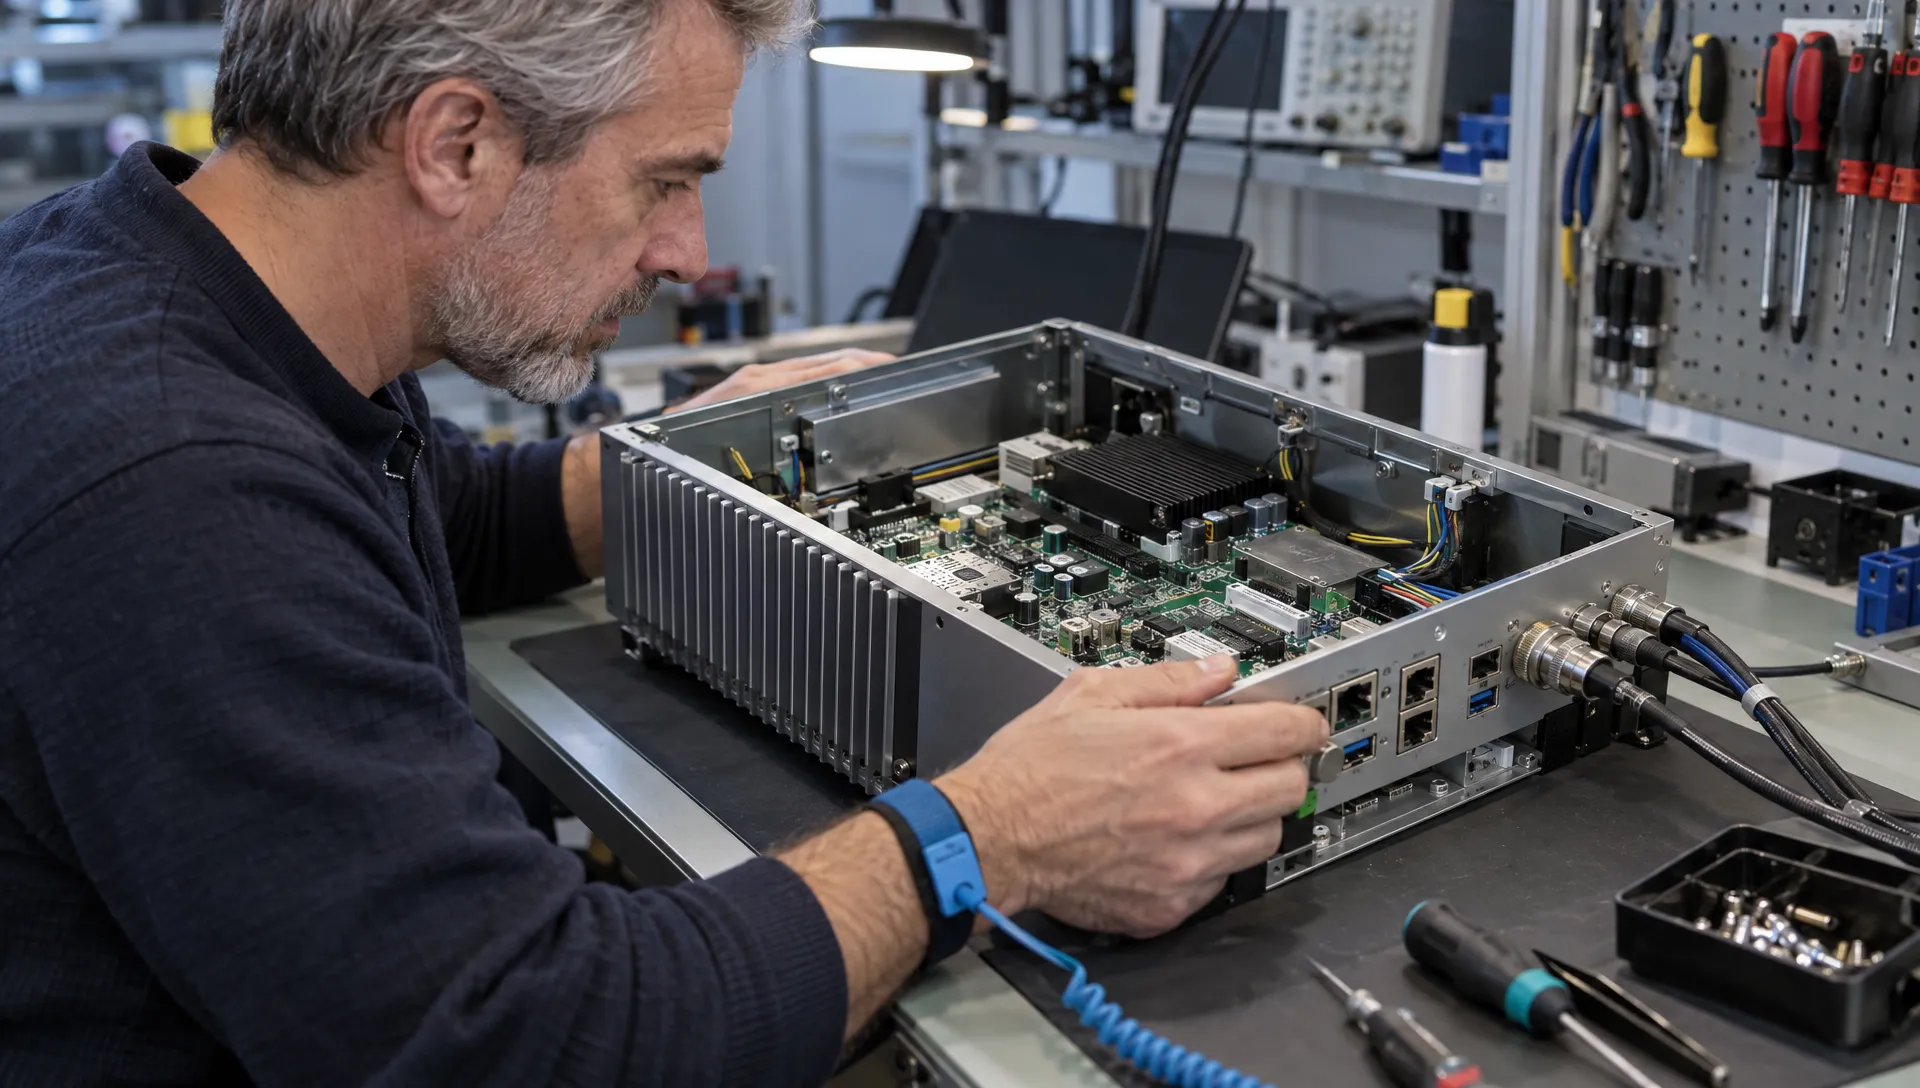
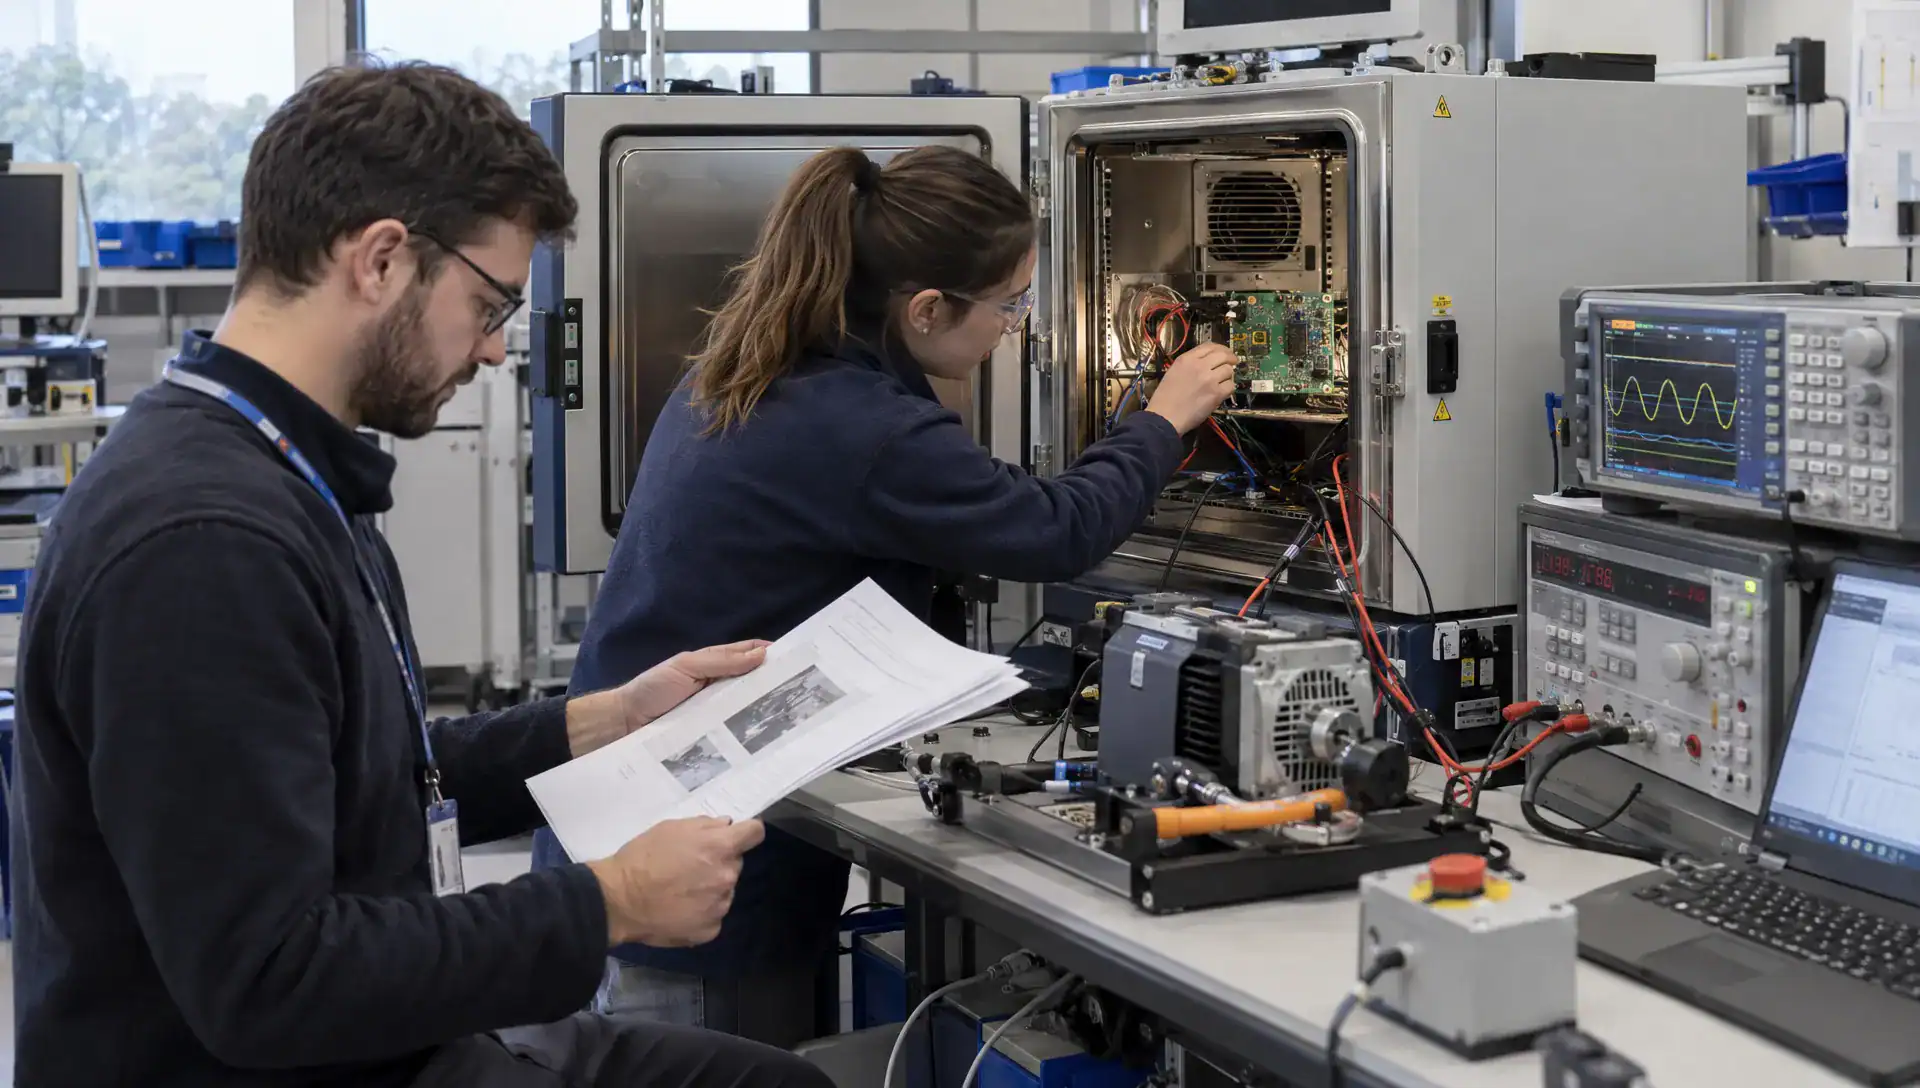
A validation plan from an electronics design company should do more than list tests. It should explain which product claims will be demonstrated, under which conditions, on which hardware and firmware versions, and what evidence will support a release decision.
For a CTO or engineering manager, the assessment question is straightforward: will this plan expose the failures that matter before the product reaches customers? A prototype that operates on a laboratory bench provides limited reassurance about installation, electromagnetic disturbances, temperature, component variation or manufacturing repeatability. The review needs to connect intended use, technical risk and measurable acceptance criteria.
Separate verification, validation and production testing
These activities answer different questions, even when organisations group them under one validation programme.
Design verification checks whether the implementation meets specified requirements. Examples include measuring converter efficiency, checking analogue measurement accuracy or confirming firmware response to a communication timeout.
Product validation checks whether the integrated product meets user needs in its intended application. This might involve operating a motor controller with representative loads, installed cabling and realistic duty cycles.
Production testing checks whether manufactured units meet defined screening criteria. It does not normally repeat every design qualification test.
Terminology varies, so assess the substance rather than insisting on particular labels. The plan should identify all three needs and explain their boundaries. A successful PCB functional test cannot replace system-level validation, while a successful field trial does not establish that every manufactured unit is correctly assembled.
What should an electronics design company document before testing?
Start with the requirements baseline. Each significant requirement needs an identifier, a source and a measurable outcome. Sources may include customer specifications, installation constraints, interface definitions, risk assessments and applicable regulatory requirements.
Ask for a traceability matrix linking requirements and risks to test procedures and eventual results. It should reveal missing coverage without requiring the reviewer to reconstruct the entire project.
| Requirement or risk | Coverage to request | Evidence expected |
|---|---|---|
| Supply interruption causes an uncontrolled restart | Defined interruption profiles during relevant operating states | Supply traces, reset logs and recovery behaviour |
| Analogue measurement drifts with temperature | Accuracy measurements across the specified temperature range | Reference measurements, uncertainty and error calculations |
| Communication loss leaves an actuator energised | Timeout and recovery tests on the integrated system | Timing records and observed output states |
| Installed cables increase electromagnetic susceptibility | Testing with representative cable lengths, loads and interfaces | Configuration records and monitored performance |
A matrix entry saying “functional test” is not sufficient. It should identify the procedure, acceptance criteria, test level and responsible owner.
Requirements that cannot yet be tested should remain visible as open items. An unresolved installation assumption must not quietly become a passed requirement simply because the bench setup was convenient.
Review the operating envelope, not just nominal performance
Ask the electronics design company to explain how its test conditions represent the real application. “Tested at full load” says little without supply conditions, ambient temperature, cooling arrangements and operating duration.
For power electronics, review input variation, load transitions, start-up, shutdown, thermal limits and fault recovery. For analogue circuits, consider source impedance, noise, calibration, temperature drift and interference from switching circuits. Embedded firmware needs coverage of timing, state transitions, watchdog behaviour and interrupted communications.
Mechanical integration also matters. An open PCB on a bench may behave differently once installed inside an enclosure with restricted airflow, long cables and shared grounding paths.
Representative scenarios might include a robot repeatedly accelerating and braking, a machine controller recovering from a supply dip or maritime equipment operating with installation-specific cable routing. These are application examples, not universal qualification requirements.
The plan should justify which combinations need testing together. Maximum ambient temperature and maximum continuous load may interact; testing them separately could miss a thermal limitation.
Simulation and modelling can identify likely worst cases and guide measurements. They should not substitute for physical evidence where enclosure effects, component variation or installation behaviour remain uncertain.
Make pass/fail criteria usable by an independent engineer
The electronics design company should define acceptance criteria before results are available. Otherwise, teams can end up rationalising unexpected behaviour instead of assessing it against an agreed requirement.
Reject phrases such as “stable operation”, “acceptable noise” or “no significant overheating” unless the plan defines them quantitatively or through unambiguous observable behaviour.
For illustration, a supply requirement might state: “The output shall remain between 4.90 V and 5.10 V at the output connector, from 100 ms after enable, across an input of 18 V to 30 V, a load of 0.1 A to 2 A and an ambient temperature of 0 °C to 50 °C.” These numbers are illustrative, not recommended limits.
That requirement still needs a procedure defining the measurement arrangement, test points, dwell conditions and treatment of uncertainty. Transient response and ripple may need separate criteria, including oscilloscope bandwidth and probing method.
For firmware, specify the permitted response to a fault, the response time and the conditions for recovery. A reset is not automatically a failure or a pass; its acceptability depends on the product requirement and associated hazards.
Where safety is involved, acceptance criteria should follow the relevant hazard analysis and applicable safety requirements. Potentially hazardous fault testing needs a controlled setup, competent personnel and appropriate protective measures.
Challenge sample selection and configuration control
Have the electronics design company justify sample quantities against the purpose of each test. There is no universal prototype count that demonstrates readiness for every product.
One unit may support early debugging. Multiple units may be needed to investigate build variation, component tolerances or repeatability. A reliability claim requires a suitable statistical demonstration, not merely several prototypes surviving a short test.
Check whether samples represent the intended production design. Record PCB revision, bill of materials, critical component alternatives, firmware version, bootloader, configuration settings and relevant enclosure details. Serial numbers should connect individual units to their histories.
The plan should distinguish deliberately selected worst-case samples from samples intended to represent normal production variation. These serve different purposes and should not be interpreted interchangeably.
Also ask how previous stress exposure affects later results. Reusing a unit after destructive testing or severe overstress can invalidate assumptions about its condition. Test sequencing and sample allocation need to account for that.
Where the final production process is not yet available, document the limitation. Hand-built prototypes can support engineering learning, but they may not demonstrate assembly repeatability or the effectiveness of production test fixtures. Evidence from representative pilot builds should close those gaps before the relevant production release decision.
Treat compliance testing as one part of the evidence
An electronics design company should identify applicable compliance obligations early and explain how they influence the validation programme. A generic promise to “test for CE” is not an adequate scope.
As the European Commission’s CE marking guidance explains, the manufacturer is responsible for identifying applicable requirements, carrying out the appropriate conformity assessment and preparing the required documentation. CE marking is not a universal third-party test certificate.
For equipment within their scope, EMC requirements and the Radio Equipment Directive may affect test coverage. Other obligations depend on the product, market and intended use. Defence, maritime and machinery applications can also involve customer-specific or sector-specific requirements.
The review should establish which tests are exploratory, which are pre-compliance checks and which will contribute to formal conformity evidence. Laboratory responsibilities, required facilities and any need for accreditation or third-party involvement should be explicit.
ProMicro’s guidance on planning electromagnetic compatibility testing before certification provides additional context for defining configurations and scheduling checks early.
Passing emissions testing alone does not demonstrate immunity, functional reliability or safe fault behaviour. Conversely, reliable operation in a field trial does not establish regulatory conformity. Keep these evidence categories connected but distinct.
Stage testing around technical risk and release decisions
The proposed sequence should show how the electronics design company will retire major uncertainties before expensive commitments. Running every test at the end concentrates redesign risk rather than reducing it.
Early work might establish the feasibility of a power stage, sensor interface or timing-critical control loop. Integrated prototype testing can then address interactions between hardware, firmware, enclosure and external equipment. Production-intent builds should support the final evidence needed for release.
Hardware-in-the-loop testing can help exercise repeatable input sequences and fault scenarios where appropriate. It still needs correlation with representative physical hardware and loads; a simulated plant does not reproduce every electrical or mechanical effect.
At each gate, state what evidence is required, who reviews it and which unresolved risks prevent progression. Fixture availability, laboratory bookings, firmware maturity and representative samples should appear as dependencies, not assumptions hidden inside the schedule.
Manufacturing readiness also needs its own evidence. Programming, calibration, production test access and fixture requirements should align with the design-for-manufacturing checks for reliable volume builds.
Finally, inspect the commercial scope. Engineering effort, test equipment, external laboratory fees, sample builds and retesting allowances should be visible. A schedule with no allowance for investigation or corrective work needs a convincing technical justification.
Require a complete evidence and change-control package
Before approving the plan, agree what the electronics design company will deliver after execution. A summary stating that all tests passed is not enough for design review, future maintenance or a later compliance investigation.
The evidence package should connect each result to its requirement, procedure revision, sample identity and configuration. It should include measured values, relevant raw data, equipment details, calibration status where relevant, deviations and the reviewer’s conclusion.
Photographs of wiring, probe positions and enclosure arrangements can be valuable when setup differences could affect results. Firmware logs and automated test scripts should have controlled versions where they form part of the evidence.
Failures need a defined route from observation to closure. Distinguish the original symptom, root-cause investigation, corrective action, repeated test and any regression testing needed to check for unintended effects.
A component substitution, PCB layout change or firmware update may invalidate earlier evidence. The plan should define how changes trigger an impact assessment and how the resulting retest scope is approved. Repeating the complete programme is not always necessary, but neither is assuming that a small change has a small effect.
Finally, make evidence access and retention explicit. Agree who receives the reports, underlying data and test assets, subject to contractual ownership and licensing arrangements.
Decide whether to approve, conditionally approve or return the plan
Assess the proposal against evidence, not presentation quality. A concise plan can be strong if the supporting procedures and responsibilities are clear. A lengthy document can still conceal missing acceptance criteria.
Ask the electronics design company to walk through one high-risk requirement from origin to release decision. Follow the requirement into the test setup, sample selection, pass/fail threshold, result record and failure-resolution process. This exposes weaknesses faster than reviewing headings alone.
Approve when coverage is proportionate to product risk, procedures are executable and responsibilities are agreed. Approval means the plan is suitable to run, not that the product has already been validated.
Conditionally approve when bounded gaps have named owners and closure dates, and the permitted work will not bypass an essential safety or technical dependency. Record which activities may proceed and which remain blocked.
Return for revision when critical requirements lack coverage, configurations are undefined or acceptance depends on subjective judgement. Do not compensate for these gaps with a promise to “resolve details during testing”.
Keep test-plan approval separate from product-release approval. At release, decision-makers need the actual results, unresolved deviations, residual risks and authorised acceptance of any limitations. Planned evidence and completed evidence are not interchangeable.
Frequently asked questions
What if the electronics design company proposes testing only one prototype? Ask what conclusions that sample supports. One prototype may be suitable for feasibility work or debugging, but it does not automatically establish production consistency or field reliability. Further sampling should follow the risks and claims being assessed.
Should validation cover every possible operating condition? Exhaustive testing is usually impractical. Require a justified combination of representative conditions, boundary cases and risk-driven interactions. The plan should make exclusions and assumptions visible rather than imply complete coverage.
Can testing start before all requirements are final? Early exploratory testing can reduce uncertainty and help establish realistic requirements. Label it accordingly. Formal acceptance requires a controlled baseline and a clear account of which evidence remains applicable after requirements change.
Who accepts unresolved risks? The project should name authorised decision-makers within the manufacturer or product-owning organisation. Engineering partners provide findings and recommendations, but release authority and responsibilities must be agreed explicitly.
Discuss validation before committing to development
A useful next discussion starts with the intended application, the highest-risk functions and the evidence needed at each release gate, not simply a requested number of test hours.
ProMicro combines embedded systems, power electronics, analogue electronics, PCB design and mechanical integration with a focus on technical risk and manufacturing readiness. Bring the current requirements, architecture and known uncertainties into that discussion so development scope, testing responsibilities and acceptance expectations can be aligned early.