In many electronics projects, the first prototype creates confidence. The board powers up, the firmware responds, sensors deliver plausible data and the actuator moves as expected. For a product development team under pressure, that moment feels like proof that the concept works.
It is proof of something, but not of everything.
A lab prototype usually operates in a controlled environment, with clean power, short cables, known users and engineers nearby. A product in the field may face voltage dips, EMC disturbances, condensation, vibration, ageing components, firmware edge cases, production spread and misuse by operators who do not know how the system was intended to behave.
That is why embedded systems design has to start from the product environment, not only from the function list. A reliable embedded product is a complete system: electronics, firmware, power conversion, analogue front ends, sensors, communication interfaces, mechanics, thermal behaviour, test strategy, compliance planning and manufacturability all influencing each other.
For technical directors, CTOs, engineering managers and founders, the practical question is not simply “Can we build a working prototype?” It is “Can we build a product that remains safe, stable and manufacturable when the ideal lab conditions disappear?”
Why lab success can hide product risk
A lab setup tends to remove the very conditions that later decide whether an embedded product succeeds. Engineers often use stable bench supplies, accessible debug connectors, short wiring and controlled temperature. Test cases are predictable and the team knows how to restart, reflash or bypass the system if something behaves unexpectedly.
In the field, the embedded system becomes part of a much less forgiving environment. A maritime device may face salt, moisture and long cable runs. A robotic subsystem may experience vibration, motor noise and fast current transients. An automotive or mobile machine product may see load dumps, cranking behaviour, temperature variation and harsh electromagnetic conditions. A connected consumer or professional device may have to handle unreliable networks, security updates and radio certification constraints.
This gap is where many expensive redesigns originate. The hardware may be functional but too sensitive to interference. The firmware may run well until a communication timeout leaves the system in an undefined state. The enclosure may look finished but trap heat around a power stage. The PCB may be easy to assemble in small quantities but difficult to test consistently in production.
A more robust development process treats the lab prototype as one milestone, not the final technical truth. ProMicro has written separately about why embedded electronics fail outside the lab, but the design lesson is broader: field performance is shaped by architecture decisions made much earlier than many teams expect.
Start with requirements that reflect real use
Good embedded design does not begin with selecting a microcontroller or drawing a schematic. It begins with understanding what the product must survive, control, measure, communicate and prove over its lifecycle.
Functional requirements describe what the product should do. System requirements describe the conditions under which it must do that reliably. Both are needed. A motor controller, for example, is not fully specified by torque, speed and interface requirements alone. It also needs defined behaviour during supply dips, blocked rotor events, thermal overload, EMC exposure, software faults, service actions and production calibration.
The most useful early requirements are specific enough to guide engineering decisions. They do not need to solve the design immediately, but they must expose the constraints that could make one architecture safer than another.
A practical requirements discussion should cover:
- Electrical environment, including supply range, transient behaviour, grounding, cable lengths and external loads
- Physical environment, including temperature, vibration, humidity, ingress risk, contamination and mounting position
- Control and safety behaviour, including fault detection, fail-safe states, watchdog strategy and operator interaction
- Communication requirements, including wired interfaces, wireless protocols, latency, range, cybersecurity and update strategy
- Production and service context, including test access, calibration, component availability, repairability and expected product lifetime
This step is often where hidden requirements surface. A customer may ask for “a wireless sensor board”, but the real challenge could be battery life at low temperature, radio performance inside a metal enclosure, certification under the Radio Equipment Directive or long-term supply of a specific sensing component.
For teams still shaping the product architecture, system design embedded thinking from day one helps prevent hardware, firmware and mechanics from being treated as separate work packages that only meet late in the project.
Architecture choices that determine field performance
Once requirements are clear enough, architecture becomes the main risk reduction tool. Architecture decides how functions are split between hardware and software, how power flows through the product, how disturbances are contained and how faults are detected before they become unsafe or expensive.
A weak architecture can still produce a working prototype. The problem is that it leaves little margin when the product meets compliance testing, production variation or real users. A strong architecture gives the development team room to tune, test and scale without redesigning the core system.
| Design area | Lab-focused decision | Product-ready design question |
|---|---|---|
| Processing | Choose the fastest available microcontroller | What processing, memory, safety, security and lifecycle profile does the product actually need? |
| Power | Use a supply that works on the bench | How will the system handle transients, brownouts, thermal load, efficiency and conducted emissions? |
| Sensing | Read the sensor successfully in nominal conditions | How will noise, drift, tolerance, calibration and mechanical placement affect measurement quality? |
| Communication | Make the interface exchange data | What happens during packet loss, bus contention, radio interference, latency or protocol mismatch? |
| PCB layout | Route the board until it fits | How will current loops, grounding, creepage, thermal paths, EMC and test access be controlled? |
| Firmware | Implement the intended sequence | How will the software recover from faults, invalid states, timing issues and interrupted updates? |
| Enclosure | House the electronics neatly | How will the enclosure affect heat, shielding, ingress, connectors, serviceability and assembly? |
These questions are not academic. They directly affect development cost and time to market. The earlier they are answered, the more options the team has. Late in the process, the same questions may require new tooling, PCB revisions, firmware rewrites or changes to supplier agreements.
Hardware and firmware must be designed as one system
In many embedded projects, problems appear when hardware and firmware are developed in parallel without a sufficiently shared model of the product. The hardware team may assume the firmware will compensate for sensor noise. The firmware team may assume the hardware will deliver stable timing and clean signals. The mechanical team may assume the electronics can tolerate heat generated by neighbouring components.
Reliable embedded systems need explicit interfaces between disciplines. That includes electrical interfaces, timing assumptions, startup and shutdown sequencing, diagnostic signals, update procedures and fault handling. If these interfaces are not defined, integration becomes discovery by trial and error.
Firmware resilience deserves particular attention. A product outside the lab must handle events that rarely appear in a simple demonstration: incomplete messages, unexpected resets, memory corruption, watchdog triggers, user interruption during an update, disconnected sensors and power loss during a write operation. The desired behaviour should be designed, not left to default processor states.
The same applies to hardware. A robust PCB is not just a carrier for components. It is part of the power, EMC, thermal and production strategy. Placement, layer stack, grounding, shielding, separation of noisy and sensitive circuits, connector choice and test point access can determine whether a design passes smoothly into validation or requires repeated corrective revisions.
Power electronics and analogue design are often the field-performance bottleneck
Digital functions are highly visible to users, but many reliability problems originate in power and analogue behaviour. Motor drives, battery interfaces, sensor front ends, measurement circuits, converters and protection stages all operate in the imperfect physical world. They are affected by tolerances, switching noise, temperature, parasitic effects and external disturbances.
For machine manufacturing, robotics, automotive, maritime and high-tech equipment, this is especially relevant. A motor drive may inject noise that disrupts sensor readings. A long cable may act as an antenna. A DC-DC converter may meet efficiency goals but create conducted emission challenges. An analogue measurement path may look stable on the bench but drift when the enclosure reaches operating temperature.
Designing for these realities requires more than choosing components from a datasheet. Engineers need to consider layout parasitics, current return paths, filtering, protection, thermal coupling, measurement bandwidth and the interaction between power stages and embedded control loops.
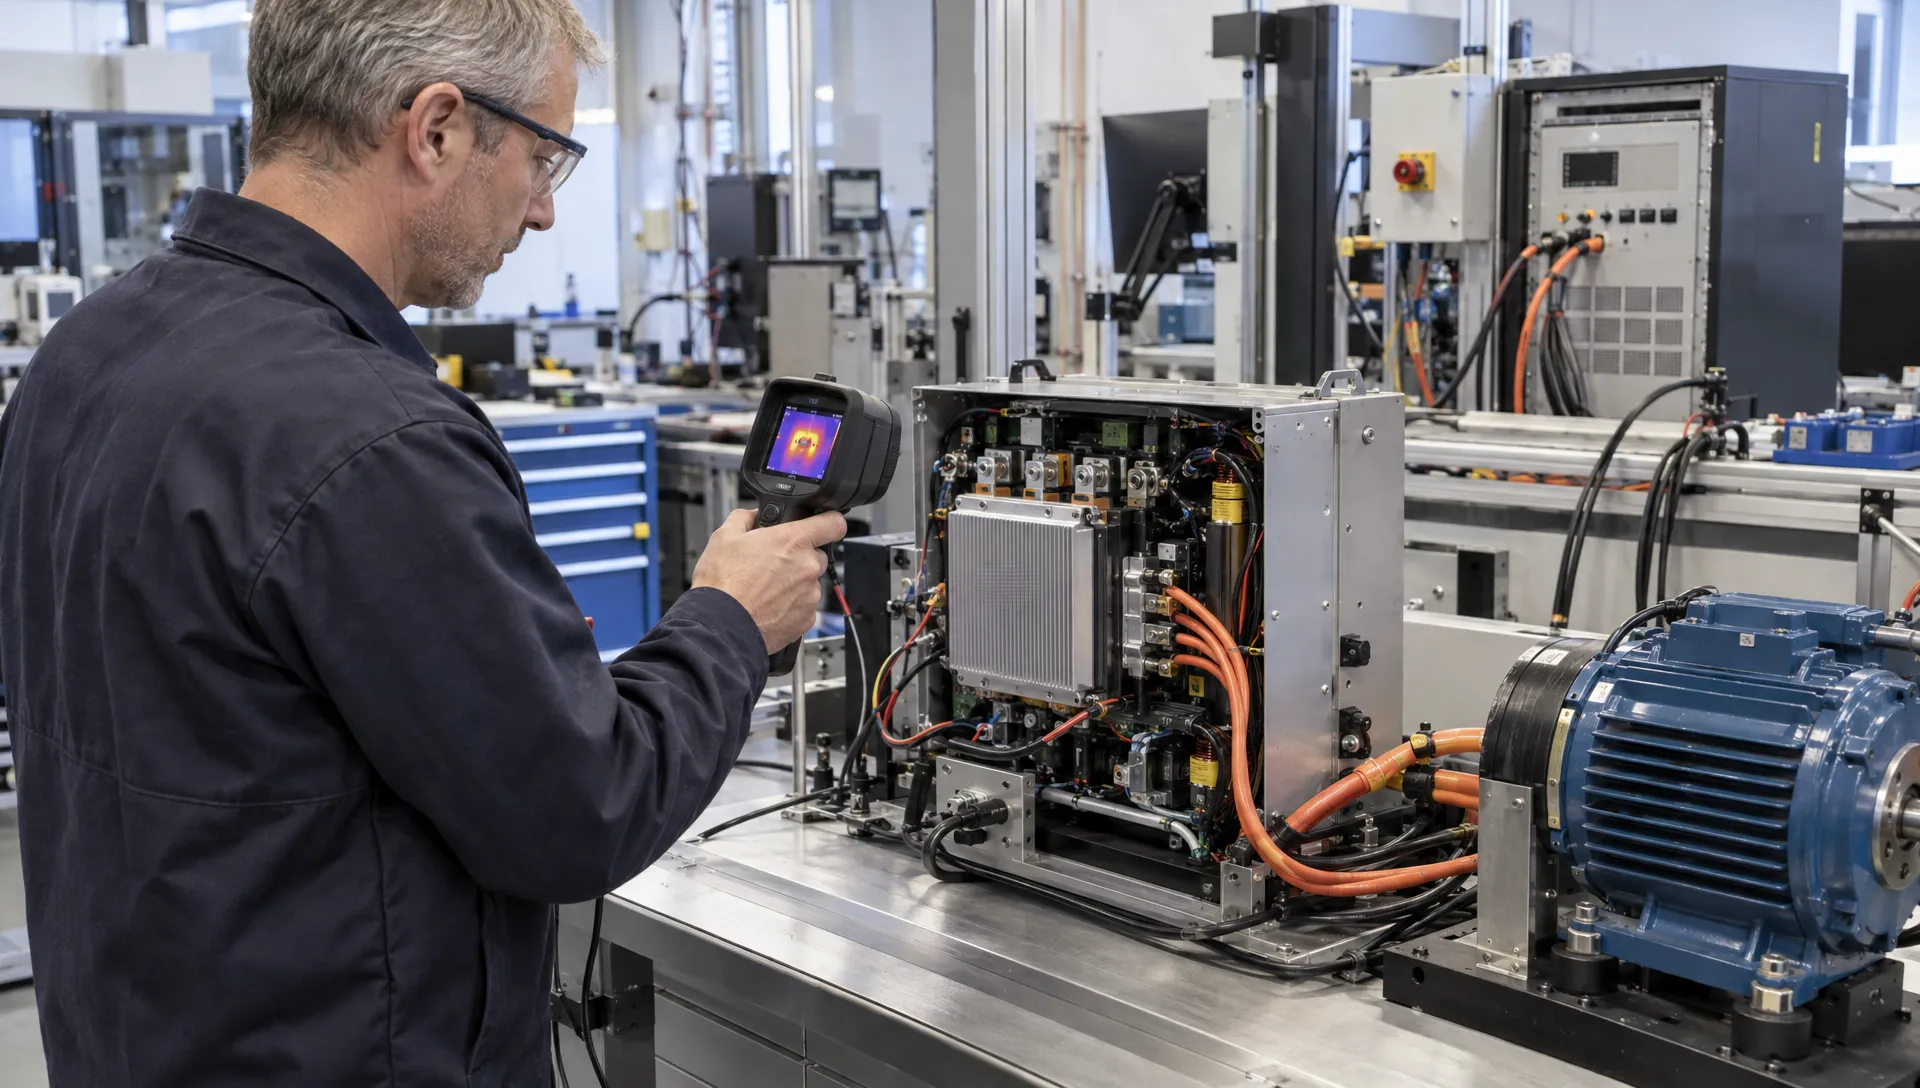
This is also where early modelling, prototype measurement and design review add significant value. Finding a noisy current loop or thermal hotspot before the PCB is frozen is far cheaper than discovering it during EMC testing or after pilot production.
Compliance should influence design before formal testing
Compliance is not a final administrative step. For embedded products sold in Europe and other regulated markets, safety, EMC, radio performance and environmental requirements can influence architecture, component selection, PCB layout, enclosure design and documentation.
For products placed on the EU market, CE marking is the manufacturer’s declaration that the product meets applicable EU requirements. The European Commission’s CE marking guidance makes clear that responsibility depends on identifying the relevant legislation and demonstrating conformity. For embedded products, that may involve EMC, low voltage, radio equipment, machinery-related requirements or other product-specific rules.
Designing with compliance in mind does not guarantee a pass result. It does reduce avoidable risk. A product that ignores EMC layout principles, shielding strategy, radio module integration rules or safety distances until the end may need fundamental redesign when testing reveals issues.
Compliance-aware design usually includes early identification of applicable standards, pre-compliance measurements where useful, documentation planning and traceability from requirements to verification. For wireless and connected devices, teams should also consider antenna placement, coexistence, firmware update mechanisms and cybersecurity expectations early enough to affect the product architecture.
From prototype to production-ready electronics
A prototype answers whether a concept can work. A production-ready design answers whether it can be built, tested, supported and maintained repeatedly.
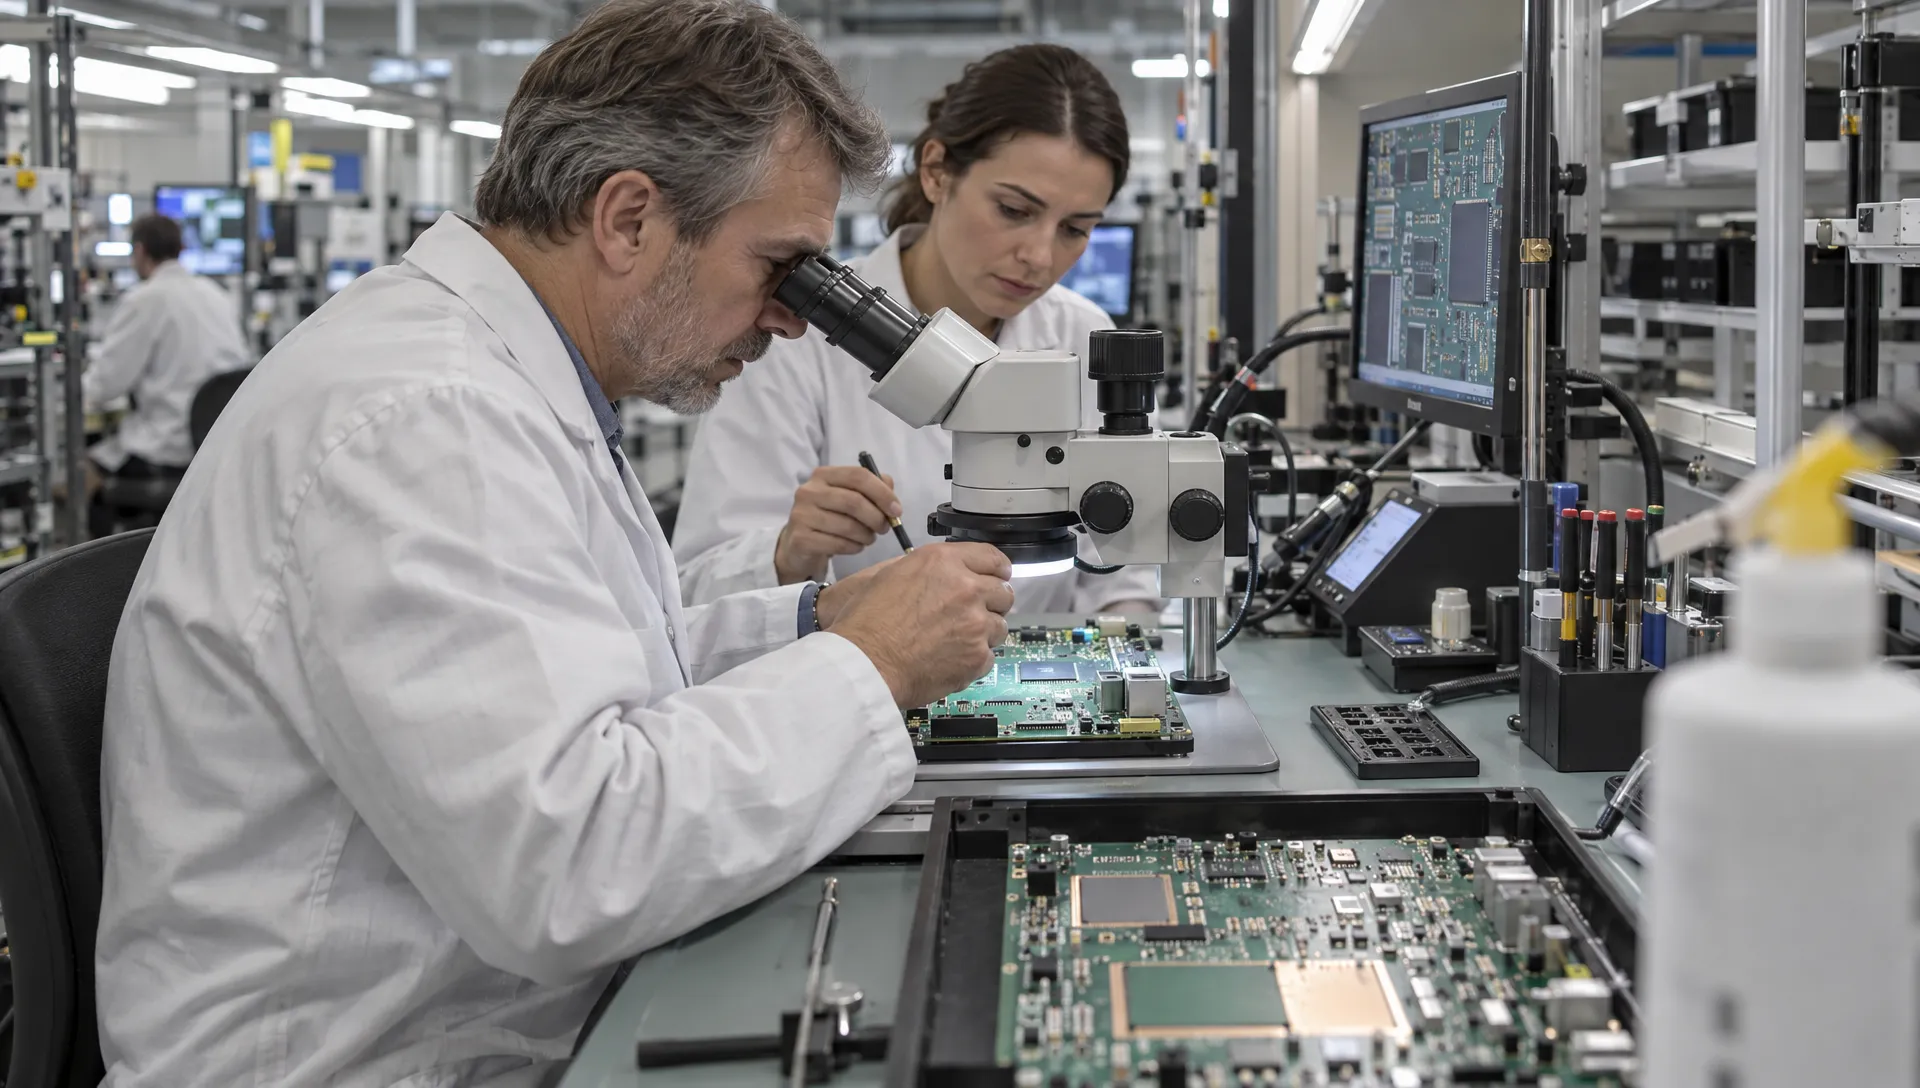
This transition is often underestimated. The prototype may use development modules, hand-soldered modifications, engineering-only connectors or components that are easy to source for ten units but unsuitable for long-term production. It may have no automated test strategy, limited diagnostics and no clear calibration process.
A production-ready embedded system needs design for manufacturing, design for testing and lifecycle thinking. That does not mean every product needs the same level of industrialisation. It means the chosen level should match the product’s risk, volume, market and expected lifetime.
| Development stage | Main question | Typical engineering focus |
|---|---|---|
| Concept | Is the product technically feasible? | Architecture options, key risks, proof of principle and requirements clarification |
| Prototype | Can the main functions be demonstrated? | Hardware bring-up, firmware basics, measurement, early integration and design learning |
| Engineering validation | Does the design meet requirements under realistic conditions? | EMC pre-checks, thermal tests, environmental exposure, firmware fault handling and system verification |
| Production preparation | Can the product be manufactured consistently? | PCB release, supplier alignment, test fixtures, documentation, calibration and assembly process |
| Lifecycle support | Can the product remain available and maintainable? | Component monitoring, firmware maintenance, redesign planning and service feedback |
This table is deliberately simple, because real projects vary. The important point is that each stage needs a different definition of “done”. A prototype that demonstrates function is not yet validated. A validated design is not yet automatically ready for repeatable manufacturing. A manufactured product still needs support when components become obsolete or application conditions change.
Verification needs to test assumptions, not only functions
Verification is most useful when it challenges the assumptions behind the design. If the team assumes a device will always have stable power, test what happens when it does not. If the enclosure is expected to protect the electronics from heat and moisture, measure that behaviour under realistic conditions. If a wireless interface is critical to user value, test interference, range, reconnection and failure modes.
A good verification plan combines unit tests, integration tests, environmental tests, electrical measurements and field-like scenarios. It also defines acceptance criteria before results are known. Without clear criteria, teams risk accepting marginal behaviour because redesign is inconvenient.
| Risk area | Verification question | Example design response |
|---|---|---|
| Power disturbance | Does the system enter a safe and recoverable state during dips or interruptions? | Brownout detection, hold-up strategy, safe shutdown and non-volatile data protection |
| EMC susceptibility | Does the product keep operating or fail safely under expected disturbance levels? | Filtering, shielding, grounding strategy, PCB separation and robust firmware recovery |
| Thermal load | Do components remain within acceptable operating limits in the enclosure? | Thermal modelling, component derating, heat spreading and layout changes |
| Firmware fault | Can the system recover from blocked tasks, invalid data or communication loss? | Watchdogs, state-machine design, diagnostics and controlled restart paths |
| Production spread | Does normal component tolerance affect performance or calibration? | Tolerance analysis, calibration routines, end-of-line tests and measurement margins |
| Lifecycle risk | Can the product survive component changes over its lifetime? | Alternative components, modular design, documented constraints and supply monitoring |
For high-value equipment, professional devices and safety-related functions, verification should be planned from the beginning. It is much easier to add test access, diagnostic hooks and logging during design than to retrofit them after the enclosure, PCB and firmware architecture are fixed.
Component selection is a long-term design decision
Selecting embedded systems technology is not only about performance. It is also about availability, support, compliance evidence, security updates, toolchain maturity and the ability to keep producing the product for years.
A processor, wireless module or power component can look attractive during prototyping but create lifecycle issues later. Some parts have short availability horizons. Some modules simplify radio development but limit antenna options or firmware control. Some components require production calibration that was not considered in the early business case.
For products expected to remain in the market for several years, technology choices should be evaluated against the full product lifecycle. That includes second-source options where possible, supplier credibility, documentation quality, qualification status and the consequences of redesign if a critical component disappears. ProMicro explores this topic further in its article on choosing embedded systems technology for long-term product success.
Long-term thinking is particularly relevant in defence, maritime, machine building, automotive-adjacent systems and professional high-tech equipment, where replacement cycles can be long and field service costs are significant.
When an external embedded design partner adds value
Many companies have strong internal engineering teams. The challenge is that embedded product development often requires depth across several disciplines at once: firmware, power electronics, analogue design, PCB layout, EMC, enclosure interaction, manufacturing preparation and compliance-aware documentation.
An external partner is most valuable when the project contains hidden technical risk or when internal capacity is stretched. That does not mean outsourcing every decision. The strongest collaborations keep product knowledge inside the customer organisation while adding specialist engineering capacity where it reduces risk most.
For example, an internal team may own the product vision, user requirements and application knowledge, while a design partner supports system architecture, PCB design, firmware development, power stage design, prototyping, EMC preparation and the route towards manufacturing. This model works well when responsibilities are clear and engineering decisions are made with the product lifecycle in mind.
ProMicro supports customers from early idea generation through electronic design, embedded system development, power and analogue electronics, PCB design, prototyping and preparation for volume solutions. The value is not only in delivering a board or a piece of firmware. It is in combining disciplines so that explicit requirements and hidden field risks are addressed before they become costly redesigns.
Practical signs your embedded product needs a deeper design review
A structured review is worthwhile before major investment in tooling, certification or production. It is especially useful when the project has moved from prototype success to broader product commitments.
Common signs include unstable behaviour during power cycling, unexplained resets, sensitivity to cable position, temperature-dependent measurement drift, communication timeouts, unexpected motor or actuator behaviour, noisy analogue readings, insufficient diagnostic data, uncertainty about applicable standards or difficulty defining an end-of-line test.
A review should not only search for faults. It should test whether the architecture still matches the product goals. Requirements may have changed since the first prototype. Production volumes may be higher than originally planned. A product that started as a simple connected device may now require stronger cybersecurity, lower power consumption or additional variants.
The earlier this review happens, the more useful it is. Before certification, it can reduce avoidable test failures. Before production, it can improve manufacturability and serviceability. Before a major redesign, it can help decide whether the issue is local or architectural.
Frequently asked questions
What is embedded systems design in product development? Embedded systems design is the process of creating the electronics, firmware, power architecture, interfaces and physical integration that allow a product to perform a dedicated function reliably. In real products, it also includes manufacturability, compliance, test strategy and long-term support.
Why do embedded prototypes fail outside the lab? Prototypes often fail outside the lab because they have not yet been tested against realistic power disturbances, EMC exposure, temperature variation, mechanical stress, firmware edge cases, production tolerances or user behaviour. The prototype may prove the concept but not the full product design.
When should EMC and compliance be considered? EMC and compliance should be considered from the architecture stage. PCB layout, grounding, shielding, enclosure design, cable interfaces, radio integration and firmware behaviour can all affect compliance risk. Formal testing usually comes later, but design decisions made early strongly influence the outcome.
How can companies reduce risk when moving from prototype to production? Risk can be reduced by defining realistic requirements, reviewing architecture across hardware and software, planning verification early, designing for manufacturing and testing, checking component lifecycle risks and involving specialists where internal expertise or capacity is limited.
Does every embedded product need an end-to-end design partner? Not always. Some teams only need specialist support for a defined area such as power electronics, PCB layout, firmware architecture or EMC preparation. An end-to-end partner is most valuable when the product combines multiple disciplines and needs to move from concept to production-ready electronics with controlled technical risk.
Build embedded products for the conditions they will actually face
A successful embedded product is not defined by a clean lab demonstration. It is defined by stable operation in its intended environment, predictable behaviour during faults, manufacturable electronics, realistic compliance preparation and support over the product lifecycle.
If your team is developing a professional device, machine subsystem, connected product or high-value electronic system, ProMicro can help turn early ideas and prototypes into robust embedded solutions designed for real use. Discuss your project with ProMicro to explore how integrated expertise in embedded systems, power electronics, analogue electronics, PCB design and prototyping can reduce risk on the path to production.